

Your access card decides who can walk through your door. A duplicate access card in Malaysia can open that same door for someone else. Some cards are easy to copy. Others are not.
Cards fall into two groups. Old cards just broadcast a number. A street copier can clone them in minutes. Newer cards prove who they are with strong encryption, so a copier can’t fake that proof. Which group is your building in?
We design access readers for a living. It’s the first thing we check on every Malaysia site visit. Two card families cause almost every problem: old 125 kHz proximity cards and MIFARE Classic cards. Harder cards use strong encryption instead. MIFARE DESFire EV3 and HID Seos are two examples. They use AES-128 (Advanced Encryption Standard, 128-bit key) encryption, and a copy shop can’t beat that math.
Key takeaways
- A 125 kHz proximity card sends a fixed ID number. A cheap hand-held tool can read and copy it.
- MIFARE Classic’s 48-bit key was broken in 2008. Treat these cards as copyable too.
- DESFire EV3 and Seos use AES-128 and a two-way check. They resist copy shops.
- A spare card should be its own credential in your system. A clone can’t be revoked on its own.
Which cards can be copied
A card that only announces a number is easy to copy. Old 125 kHz proximity cards and fobs work that way, so a copy shop clones them in seconds. MIFARE Classic cards use a weak cipher that was broken years ago, so treat them the same way. Cards with AES encryption and a two-way check are the hard ones. A shop can’t fake that check.
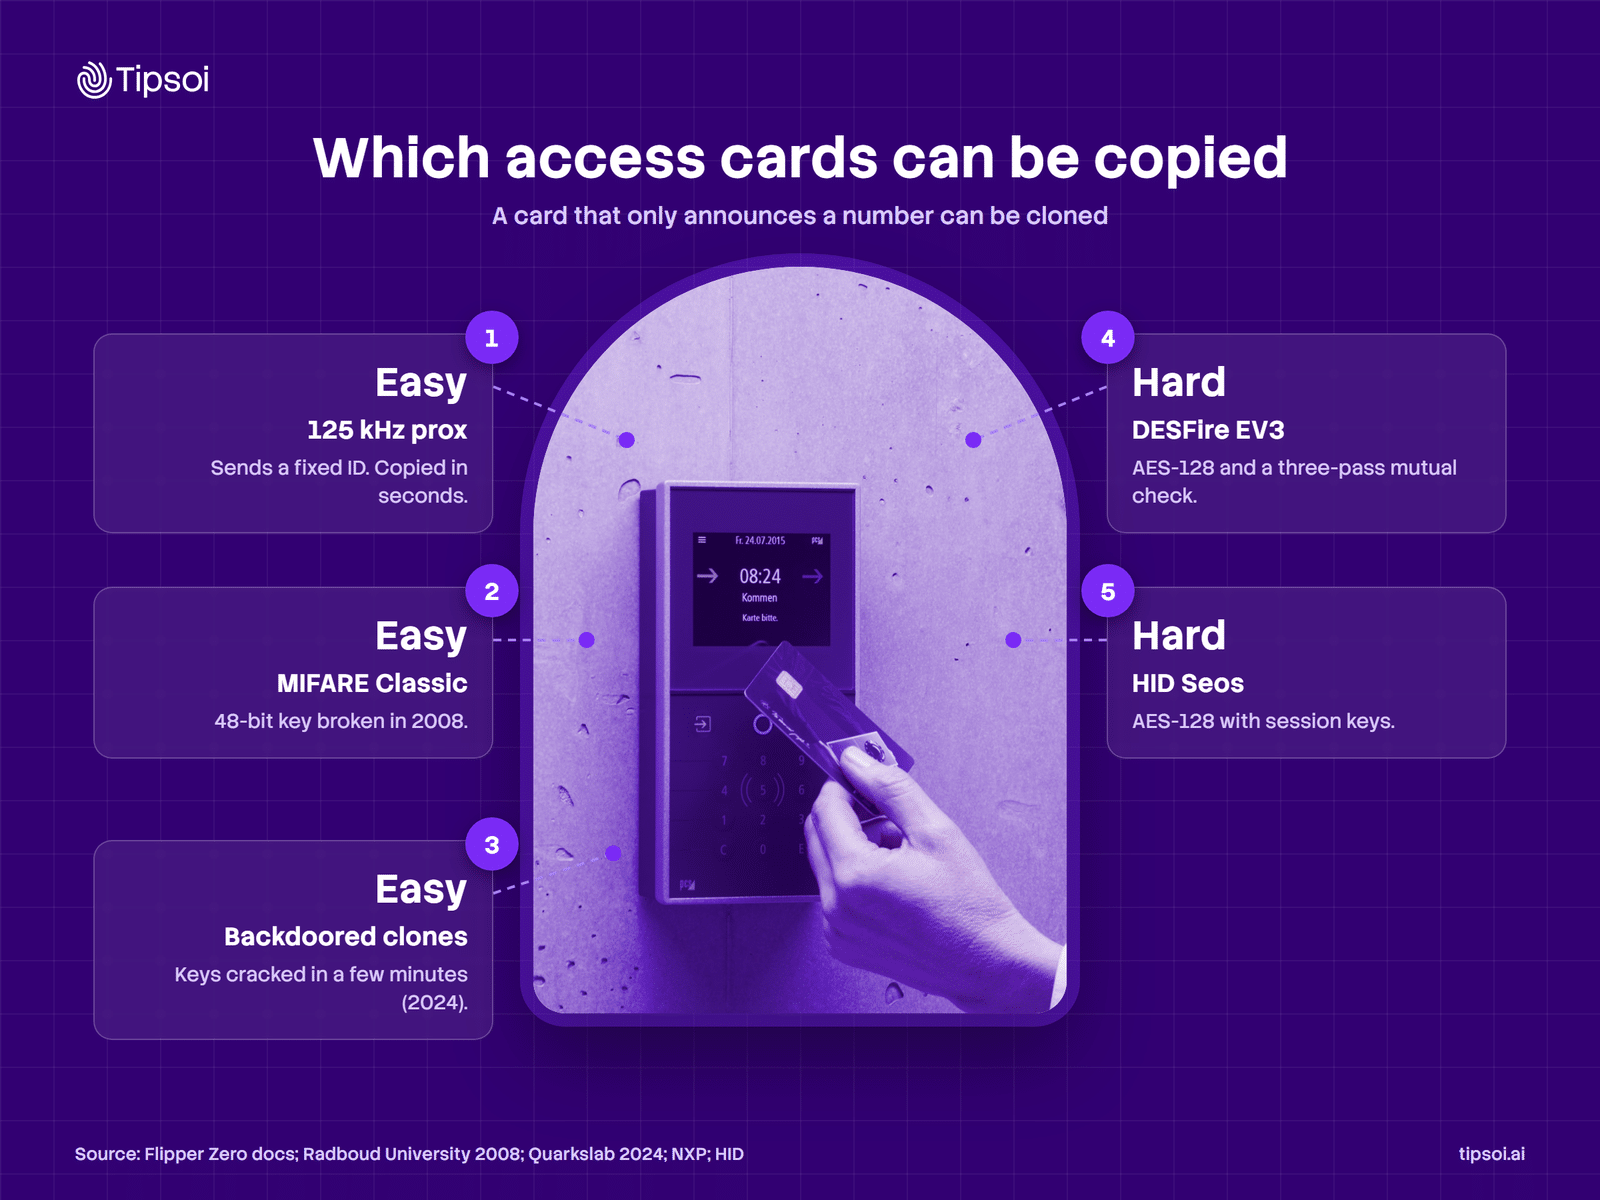
The table below shows five card families found in Malaysian offices and condos.
| Card type | How it proves itself | Can a shop copy it? |
|---|---|---|
| 125 kHz proximity (EM4100, HID Prox) | Sends a fixed ID number | Yes, in seconds |
| MIFARE Classic (13.56 MHz) | Crypto1 cipher, 48-bit key | Usually yes |
| Backdoored MIFARE Classic-compatible chips | A 2024 hardware backdoor skips the cipher check | Yes, in minutes |
| MIFARE DESFire EV3 | AES-128, three-pass mutual check | No, with keys set well |
| HID Seos | AES-128, session keys | No, with keys set well |
MIFARE Classic fell early. In 2008, Radboud University researchers showed its 48-bit key can be cracked in under a second.
Newer attacks keep coming. In August 2024, Quarkslab found a hardware backdoor in common MIFARE Classic-compatible chips. It cracks all their keys in a few minutes. That’s the third row in the table above.
Free download: Which Card Type Do You Have? A 30-Second Check
A one-page PDF built from the table above, with the same five card types and three quick questions you can check against your own card. Print it or send it to your facility or IT team.
Who actually clones a card
Two different people clone a card. Knowing which one you’re facing changes how urgent the fix is.
A copy shop clones a card for a small fee, no questions asked. Most copy shops aren’t criminals. They cut house keys and copy cards all day, and a weak card looks the same as a house key to them. The risk is simple: anyone who borrows your card for a minute, a visitor, a contractor, a former staff member, can walk out with a working copy.
A targeted attacker wants into one specific building. They don’t need a shop at all. A hand-held reading and cloning tool, such as the Flipper Zero, copies a weak card on the spot. No help from anyone else is needed.
Two card types carry this risk: 125 kHz proximity cards and MIFARE Classic cards. Both use weak or no encryption, so an attacker can duplicate either one in minutes.
How to stop cloning
You can stop cloning in three steps. First, move to an encrypted card with a mutual check. Second, protect the cable between the reader and the controller. Third, add a second factor at your highest-risk doors. Then roll the change out door by door.
Start with the card. NXP’s MIFARE DESFire EV3 uses AES in hardware, with a 128-bit key and a three-pass mutual check. NXP’s own MIFARE Classic product page tells buyers to use DESFire or MIFARE Plus for security needs.
Next, the wire. A 2025 Axis white paper notes that Wiegand wiring sends data in plain text. OSDP (Open Supervised Device Protocol) Secure Channel encrypts that same link with AES-128.
Then add the second factor. Our FastFace 8 FTC reads your access card through an embedded HID module, then checks the person’s live face at the door, with anti-spoofing. It’s Lenel OnGuard compatible, so it can sit inside an access system you already run. A copied card alone still won’t open the door: the face has to match too.
FastFace 8 FTC is one part of a full access control system. See how it fits your building, floor by floor, with no downtime.
Why issue safe spare cards
A safe spare card is its own credential, issued and named by your access system. Each card gets its own number, its own doors and its own line in the log. Lose one, and you revoke only that card. A clone shares the original’s number instead, so revoking it locks out the real owner too.
Speed matters as much as the card itself. BRAC Bank in Bangladesh runs Tipsoi on 843 devices at 647 locations, as of November 2026. Our 2026 company profile records a nationwide card revocation there in about 60 seconds. Our Unauthorized Logs report then lists every refused attempt, so a stale or copied card shows up fast.
Set two simple rules for your own building. Only your management office issues spares. Every spare carries a name and an end date.
Why copies are a risk
A duplicate access card opens the same doors as the real one. It leaves the same name in the log too. So a lost card shows up as a gap, while a cloned card shows up as a normal entry. You only learn about it after something goes wrong, when the log points at the wrong person.
NIST, the U.S. National Institute of Standards and Technology, reached the same view about a card number used alone. NIST SP 800-116 Revision 1 (2018) says a card number that anyone can read can be cloned easily. It rates that check as giving “little or no” confidence, and it asks for cryptographic authentication instead.
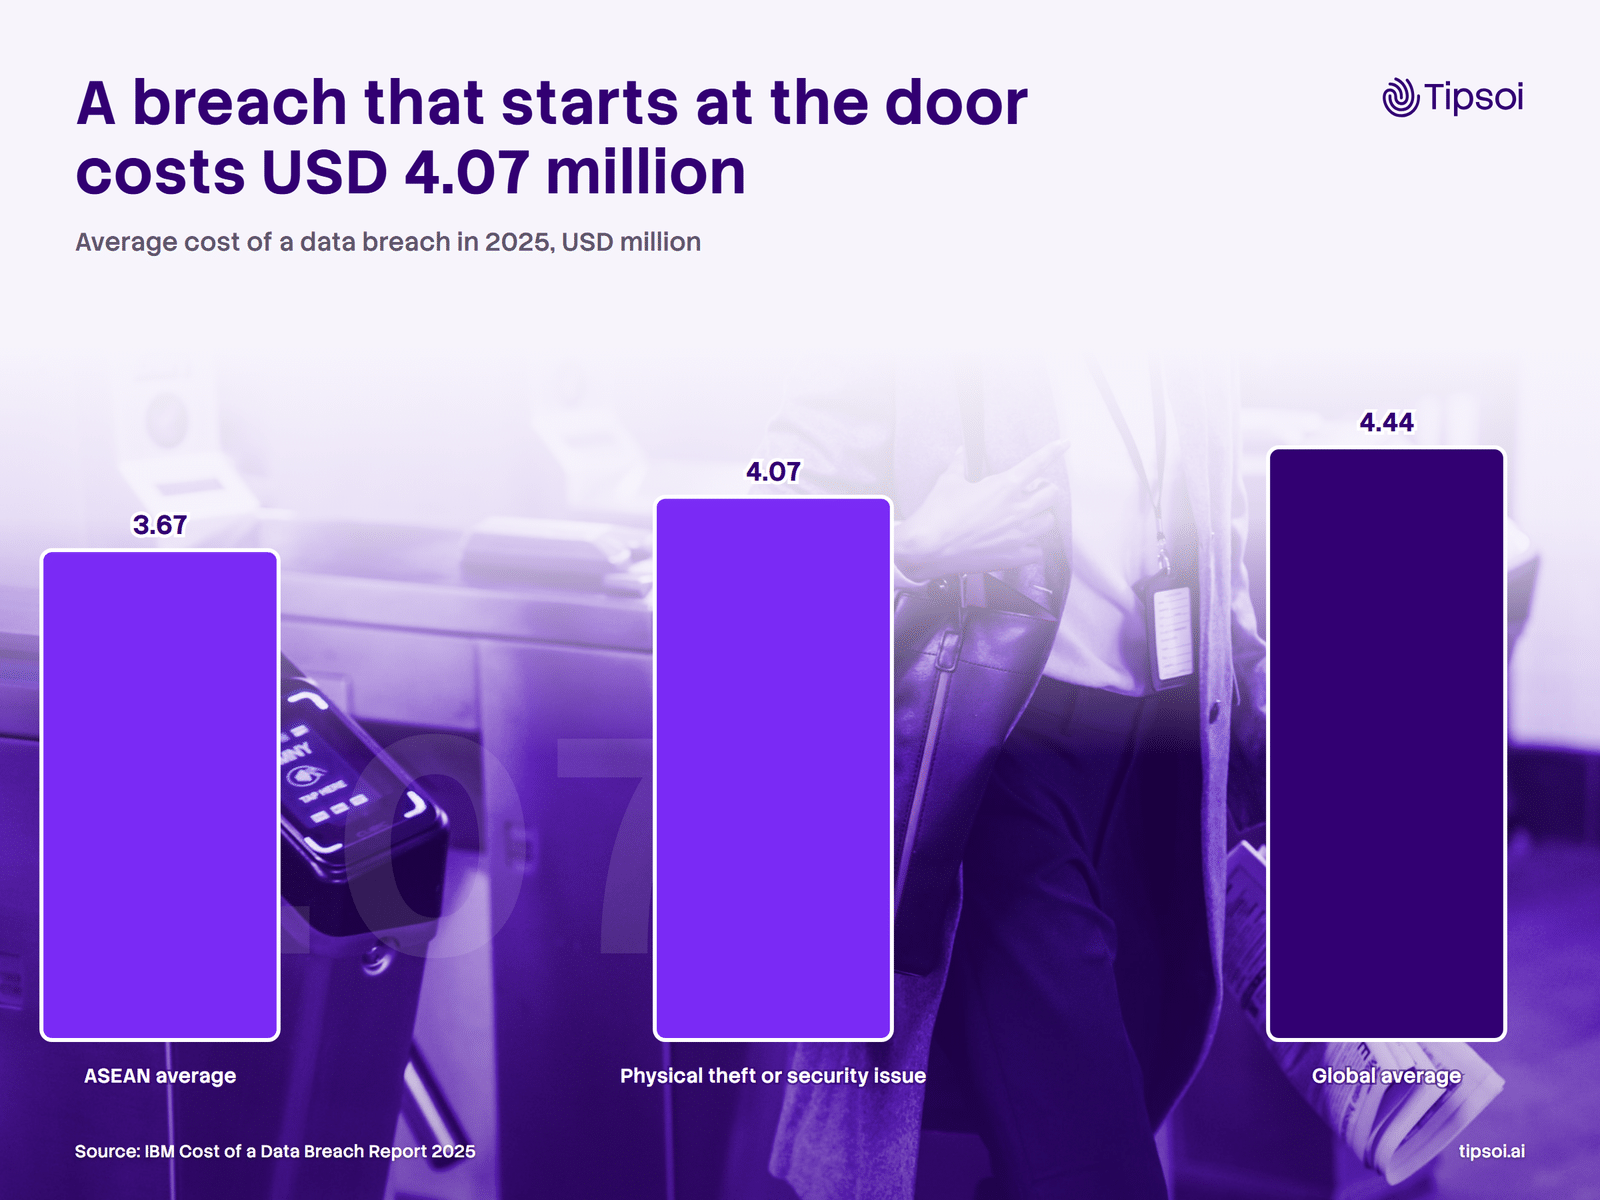
A breach that starts at the door is expensive. IBM’s 2025 breach report puts breaches that began with physical theft or a security issue at USD 4.07 million on average, worldwide. For ASEAN, a group that includes Malaysia, the same report gives USD 3.67 million.
There’s a legal side too, and it carries real weight in Malaysia. In September 2025, Bukit Aman’s Commercial Crime Investigation Department warned that selling or owning a card-cloning device is illegal. Police can investigate it as cheating under Section 420 of the Penal Code, and the Computer Crimes Act 1997 can also apply. So a duplicate card from a street shop puts your organisation at legal risk too, not only a security one.
FAQ
Can every duplicate access card be made in a shop?
No. A 125 kHz proximity card and most MIFARE Classic cards can be copied fast. Encrypted cards such as MIFARE DESFire EV3 and Seos use AES-128 and a two-way check, so a copy shop can’t clone them when the keys are set up well.
How do I know if my access card can be copied?
Check the card, or ask your management office for its type. A card marked 125 kHz, EM or Prox can be copied. If a local shop copies it in minutes, that confirms it. DESFire and Seos cards are the safer ones.
Is it legal to duplicate an access card in Malaysia?
Not for someone else’s card. Police warned in 2025 that selling or owning a card-cloning device is illegal, and it can be investigated as cheating under Section 420 of the Penal Code. Your building rules may ban copies too. Ask your management office for an issued spare card instead.
Can I copy my access card to my phone?
Some phones can copy a simple 13.56 MHz card, but that’s a risk, not a shortcut. Your access system can’t tell a phone copy from the real card. Use a mobile credential that your own access system issues instead. It can be revoked on its own. A copy can’t.
What should a building do after finding a cloned card?
Revoke the card number right away, then issue the owner a new one. Check the access log for entries the owner didn’t make. Then move your highest-risk doors, the ones guarding data, cash or residents, to encrypted cards.
Next step
If your cards are 125 kHz or MIFARE Classic, a stranger can clone one in a few minutes with a cheap reader. Start with the doors that guard your data, cash or server room: move those to an encrypted card before any other project.
For the fuller picture, read our access control system guide for Malaysia, our guide to RMiT and PDPA 2024 at the door, our guide to biometric attendance tracking in Malaysia, and our Malaysia overview. Blueberry Technologies Sdn Bhd, our partner on the ground in Malaysia, handles installation and first-line support.
Ready to see it work? A short demo shows how one reader can take you from an old card today to a secure one, one wing at a time, without a single day of downtime.
Free demo, no obligation. Most sites go live in about a week.