

RMiT physical security comes down to one question at the door: can you prove who went in, why, and for how long? Bank Negara Malaysia reissued RMiT on 25 September 2026, and the privacy law now treats face data as sensitive. Below, each rule gets an example.
Bank compliance heads ask me this often, because we run access control for banks with hundreds of branches.
Key takeaways
- Lock the data centre to anyone without a reason to be there.
- Every pass should match a job and end on its own.
- RMiT keeps key system logs for three years, so keep data centre door logs as long.
- Face data is now sensitive, and a breach must reach the Commissioner within 72 hours.
RMiT in plain words
RMiT is Bank Negara Malaysia’s rule book for technology risk. It binds banks, insurers, takaful firms and some payment firms. At the door it asks three things: keep outsiders out of the data centre, give each person only the access they need, and keep the record.
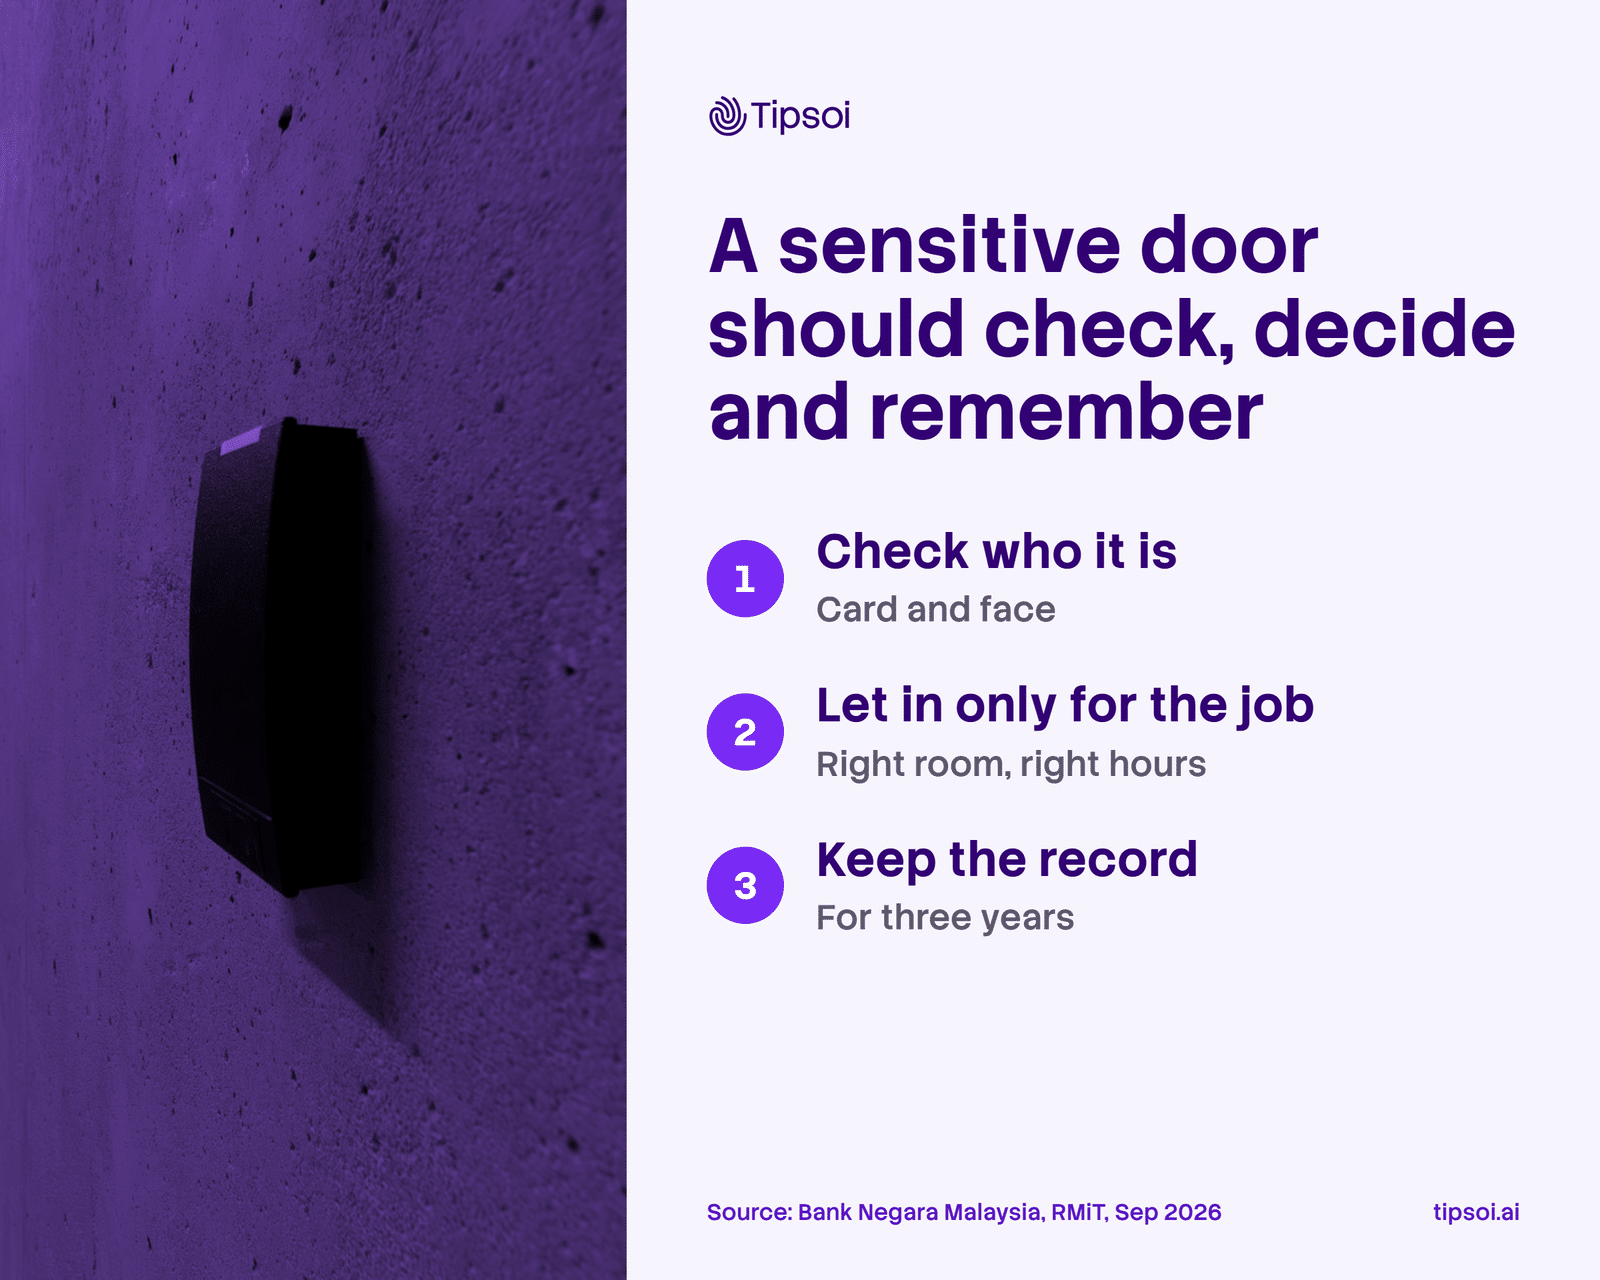
The current text is the RMiT policy document reissued on 25 September 2026. Its paragraph 4.1 still gives 28 November 2025 as the date it took effect, unless a clause says otherwise.
Under paragraph 1.3 of the 2026 policy, BNM can act against the firm and its directors. So a weak door is a board risk.
Four door rules
Four RMiT physical security rules decide how a bank’s sensitive doors behave. First, lock the data centre. Second, fit access to the job and end it on time. Third, a face or fingerprint may be one of the checks. Finally, keep logs for at least three years.
1. Secure the data centre
Clause 10.26 of the 2026 RMiT says you must secure the data centre from unauthorised access. For example, a courier who drops a server at the loading bay should not be able to walk on into the data hall.
2. Give access for the job, then end it
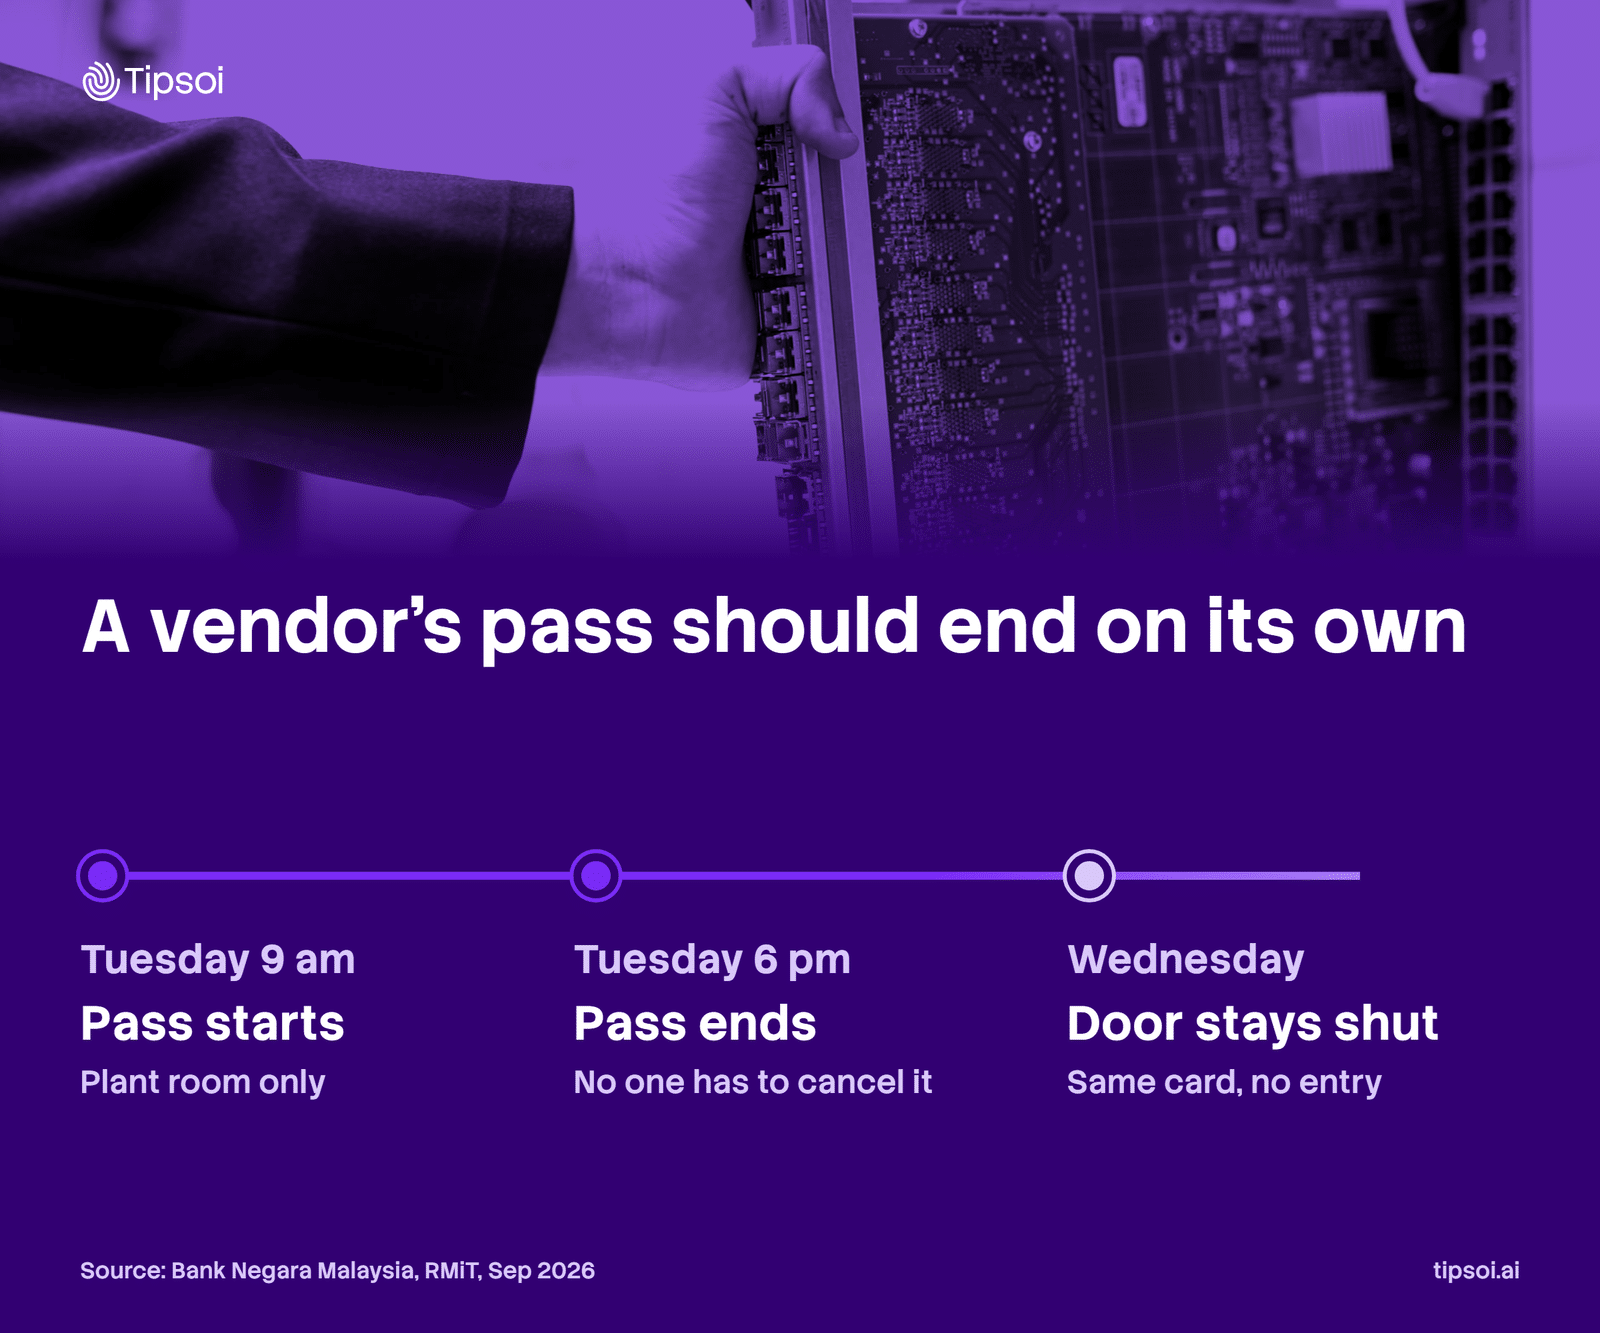
Clauses 10.54 and 10.28 ask for time-bound access, and vendor access that is approved and watched. For example, a cooling engineer booked for Tuesday gets a pass for the plant room only, from 9 am to 6 pm. On Wednesday the card opens nothing.
3. Stop the shared card
Clause 10.55 allows a biometric trait as one factor in a multi-factor check. For example, if a staff member lends a card to a colleague, a card-only door lets the colleague in. A card-plus-face door refuses, because the face doesn’t match the card.
4. Keep the record for three years
Clause 10.57 of the September 2026 text keeps activity logs for at least three years. For example, an auditor asks who entered the data hall in the last 90 days, and who was refused. You should answer from one export, in minutes.
RMiT sets no fixed time for door logs, so we suggest three years for data centre and vault doors too.
Visitors and cameras
The 2026 reissue added Appendix 12, a code for banks and insurers officially designated as critical infrastructure. It names ID badges, biometric systems, visitor logs with escorts, turnstiles or electronic locks, and CCTV footage kept for at least 30 days. You also review the plan every year.
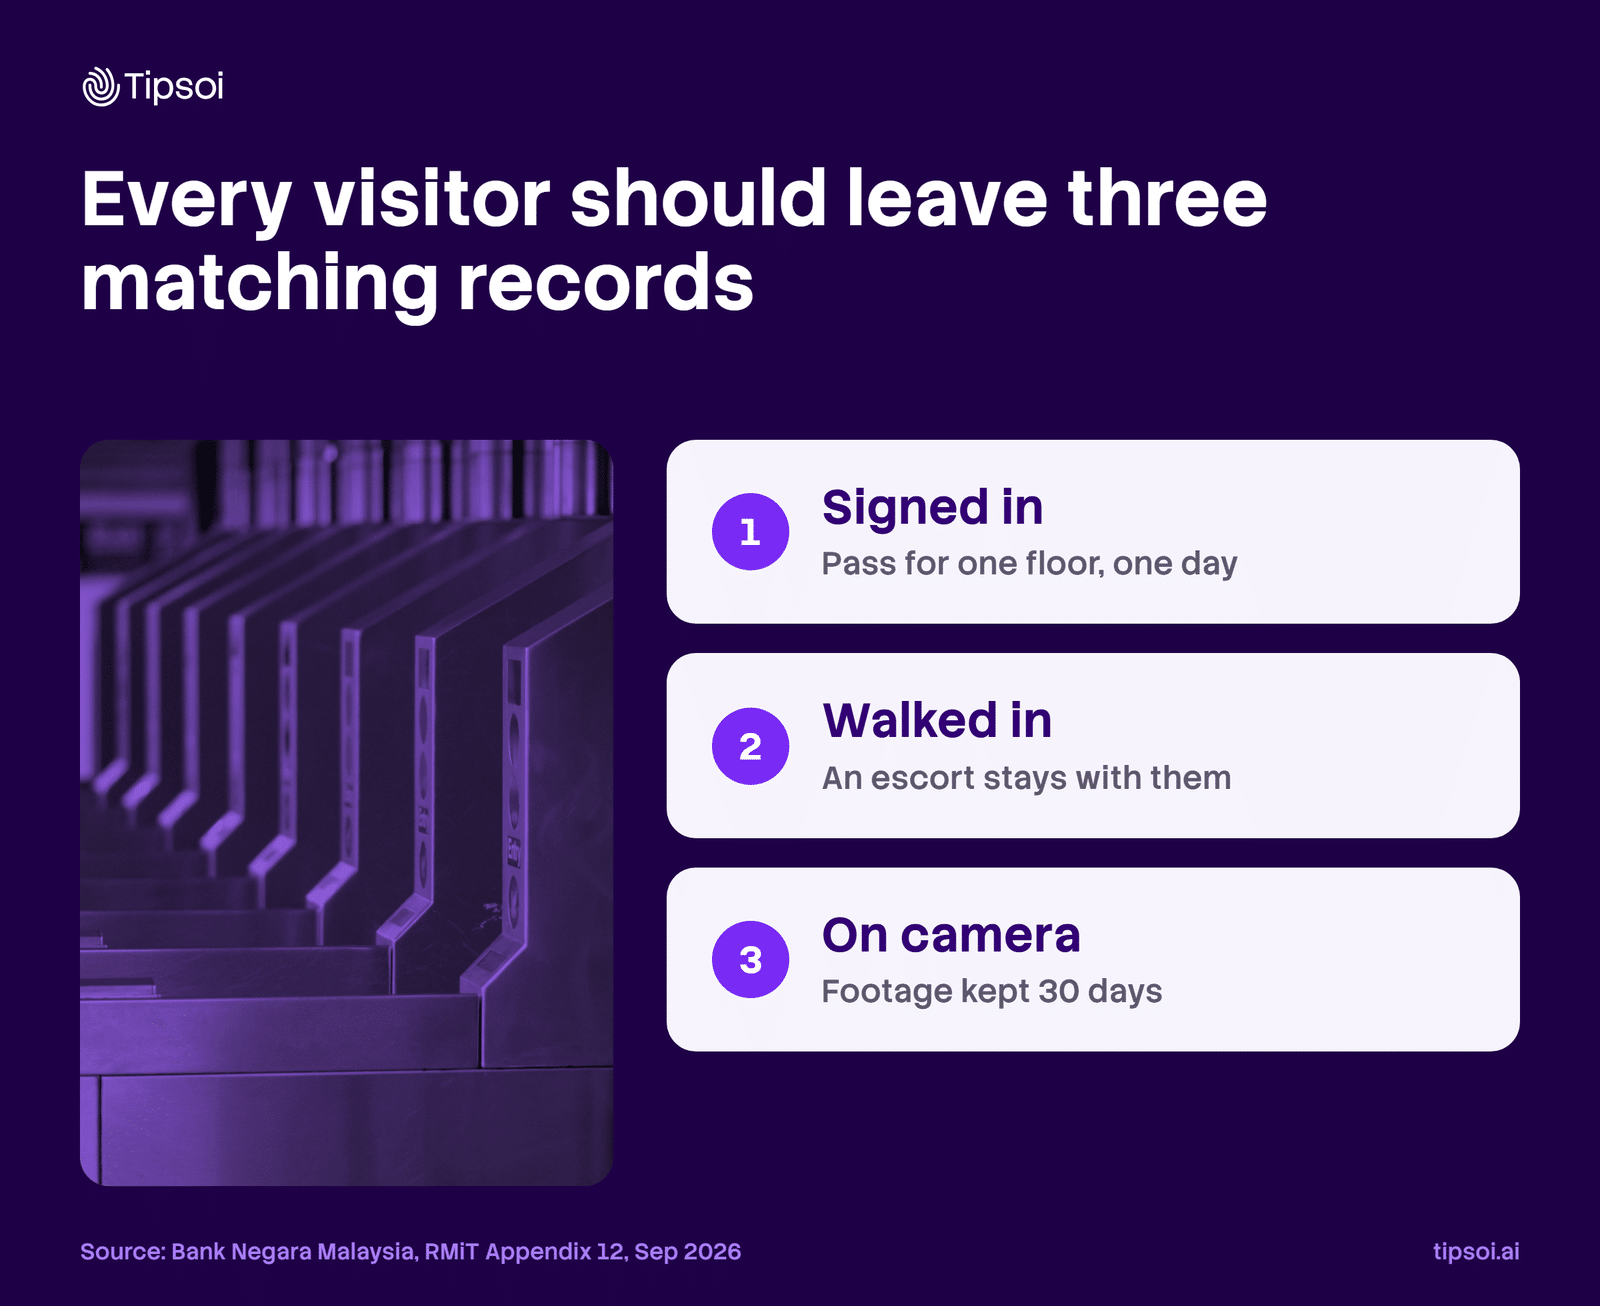
Clause 13.1 of the 2026 Appendix 12 asks for a written physical security plan. For example, a visiting auditor signs in, gets a pass for one floor, and an escort walks with them. Later, the pass record, the escort’s name and the footage should all match.
Clause 13.2 keeps CCTV footage for at least 30 days. For example, if someone forces a branch server room door on a Saturday, the footage must still exist when the review starts. The code sits under the Cyber Security Act, in force since 26 August 2024.
The privacy law
Parliament amended Malaysia’s Personal Data Protection Act, and three changes reach the door. Biometric data became sensitive data. The top fine rose to RM1 million. Also, you must now report a data breach to the Commissioner within 72 hours. So a face reader at a branch needs the same care as health records.
The amending Act A1727 got Royal Assent on 9 October 2024. From 1 April 2025, biometric data became sensitive and the top fine rose from RM300,000 to RM1 million. For example, a server with face templates for 5,000 staff holds sensitive data on 5,000 people.
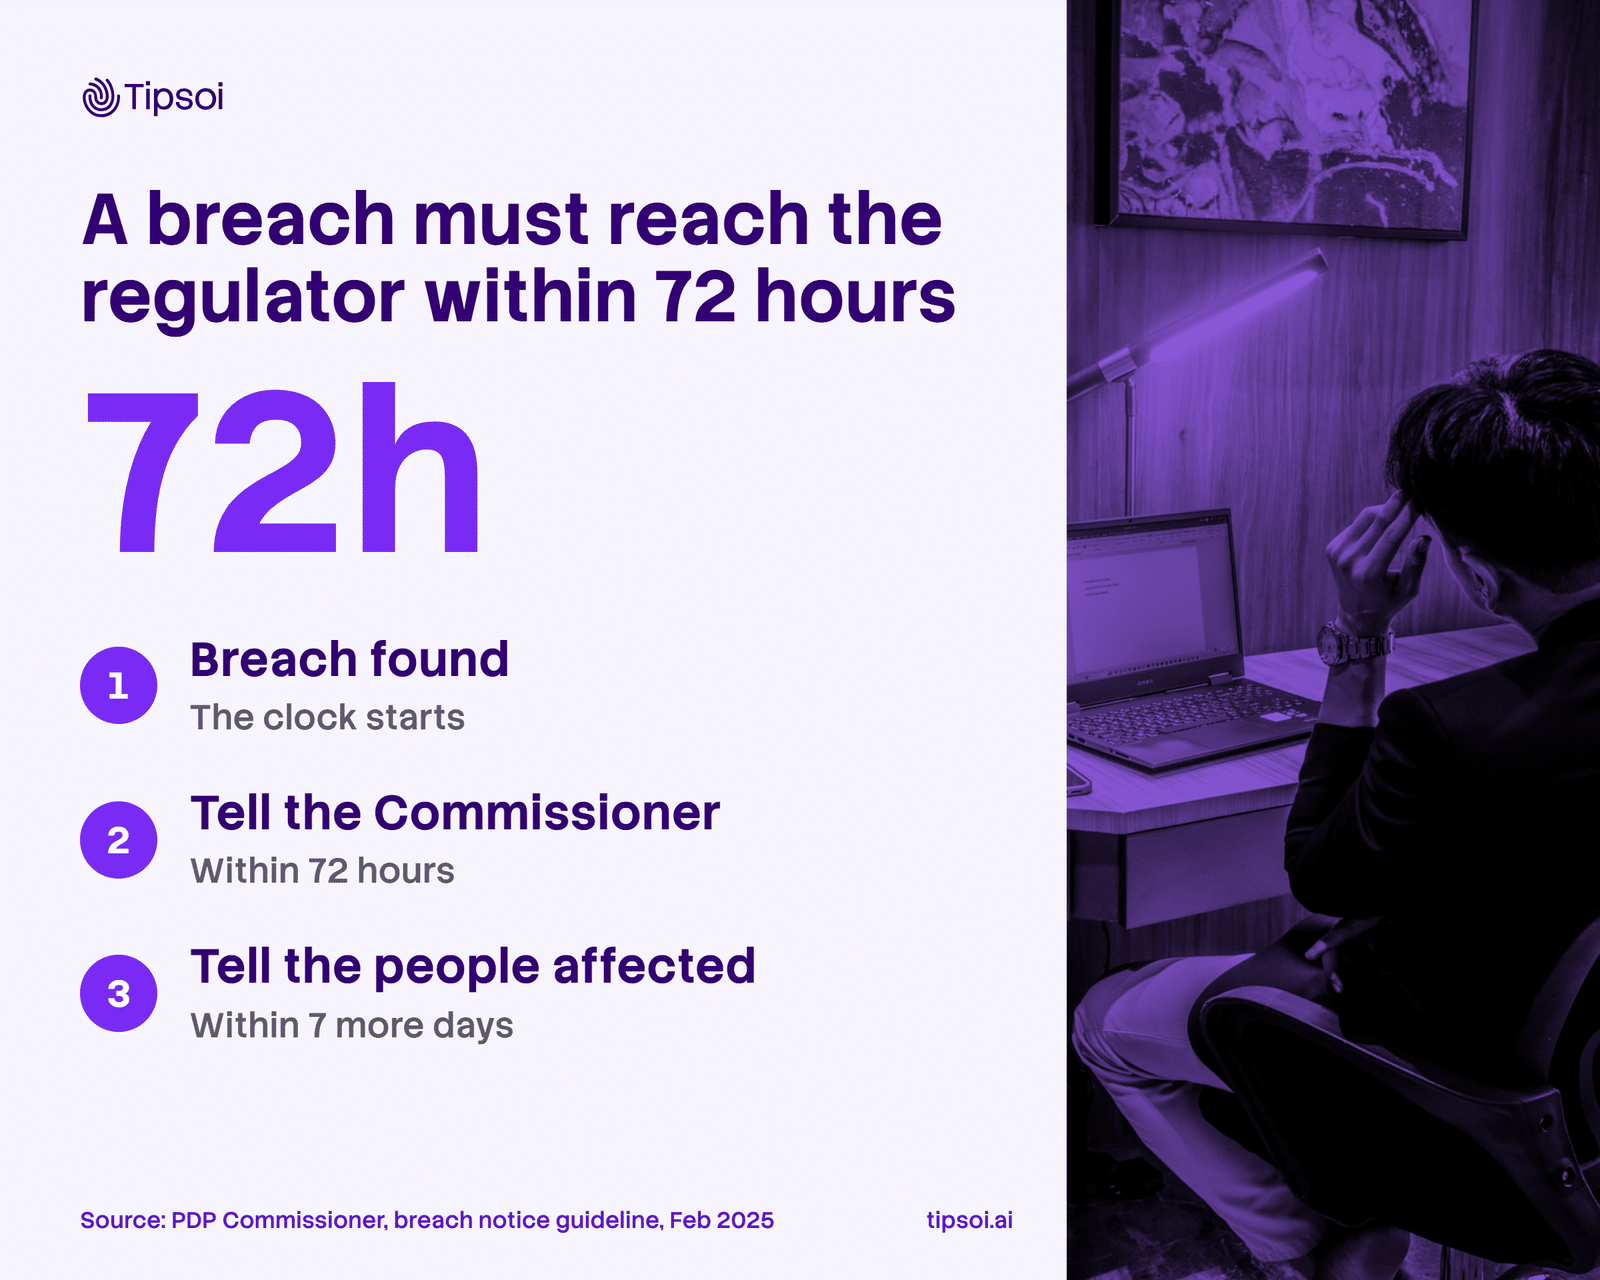
The breach notice guideline of February 2025 sets a 72-hour clock. For example, a breach found on a Friday night must reach the Commissioner by Monday night. If the harm is significant, the people affected hear within 7 more days. Face templates count as significant.
Proof auditors ask for
An auditor won’t accept a policy alone. They ask for the record behind each rule. So every duty needs a door setting that enforces it and an export that proves it. If you can’t produce a record in the last column today, that row is your gap.
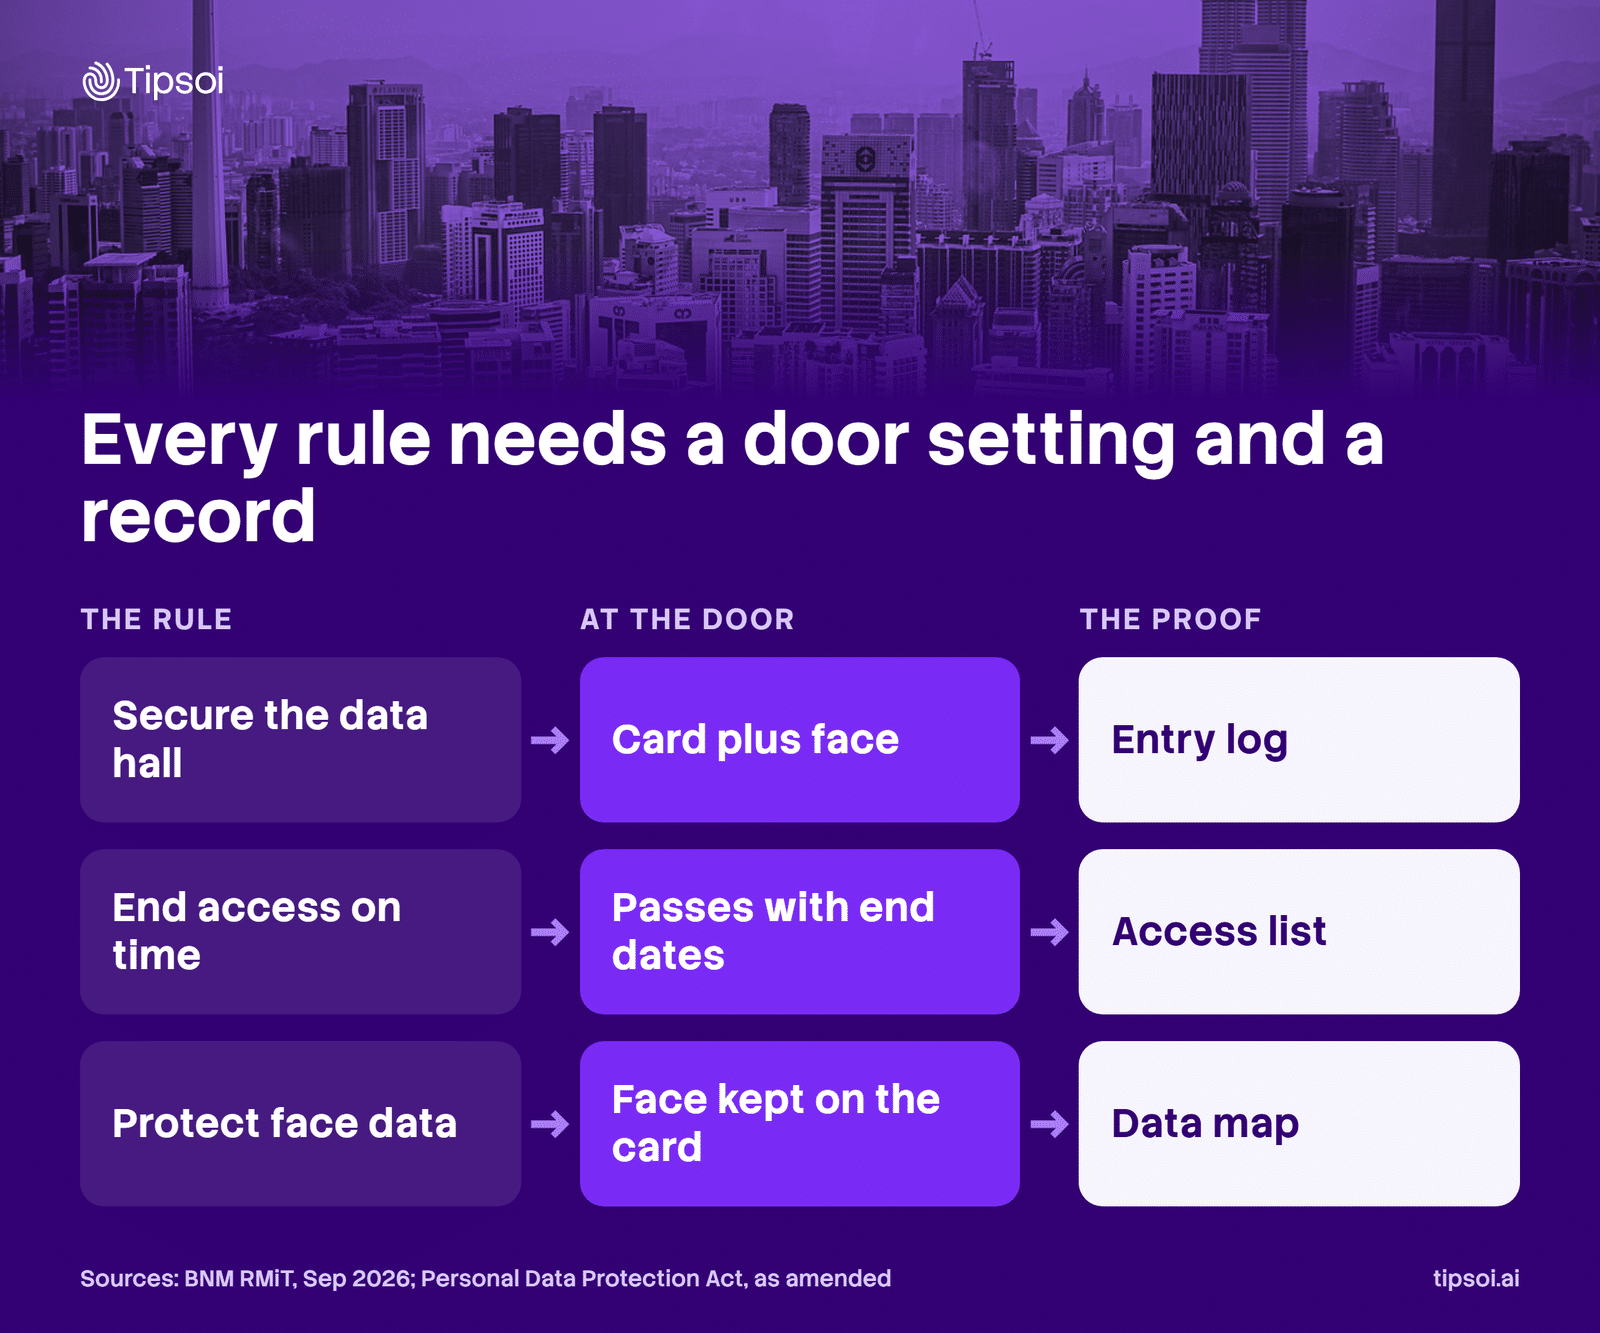
| Rule | Door setting | Record to keep |
|---|---|---|
| Secure data centre | Card plus face at data hall doors | Entry and refused-entry logs |
| Least privilege | Passes by role and zone, with end dates | Access list export |
| Face data is sensitive | Face template kept on the card | Data map and impact assessment |
| 72-hour breach notice | Central logs searchable by person and door | Incident timeline |
We built our own reader for this. On the FastFace 8 FTC, we write the face template to the staff card, so the reader and server keep no face data. So if attackers break into a server, there are no face templates on it to lose.
Leavers are the other weak point. At BRAC Bank, across hundreds of branches, our platform runs in the bank’s own data centre. Our 2026 company profile records a pass revoked network-wide in about 60 seconds. IFIC Bank runs its HID readers and our devices on its own network.
FAQ
Does RMiT physical security require biometric access control?
No. RMiT asks for a secure data centre, least privilege and logs. It allows biometrics as one factor in a check, and Appendix 12 lists biometric systems next to ID badges.
How long should a bank keep door access logs in Malaysia?
RMiT sets no fixed time for door logs. It asks three years for key system logs and 30 days for CCTV. So many banks keep data centre door logs for three years.
Is biometric data sensitive personal data under the PDPA?
Yes. Since 1 April 2025, the amended PDPA lists biometric data as sensitive personal data. A breach of it counts as significant harm.
Who does RMiT apply to?
It covers licensed banks, Islamic banks, insurers, takaful firms and development finance institutions. It also covers some e-money, payment and remittance firms.
What is the PDPA penalty for a data breach?
Breaking the data protection principles can bring a fine of up to RM1 million, three years in jail, or both. Failing to report a breach can bring up to RM250,000.
Next step
Start your RMiT physical security review with your data centre and vault doors. Check who can enter, when each pass ends, and whether you can pull 90 days of logs in an hour. Read our access control system guide for Malaysia, our guide to duplicate access card risk and our Malaysia overview. Tipsoi is ISO 9001:2015 and ISO/IEC 27001:2022 certified.
A short demo shows the logs and the card-based face check side by side.
Free demo, no obligation. Most sites go live in about a week.
This guide is for planning, not legal advice.